

Kubernetes User Namespaces Are Here and Might Break Things First
Six years of work, dropped into production overnight
After six years of development, testing, iteration, and probably a lot of second-guessing, user namespaces in Kubernetes didn't arrive with fireworks. They just showed up. A core contributor dropped three dense blog posts, ranging from basic usage to gritty implementation details, for people who care how the machinery works.
You can feel the intention behind it. This was built for engineers who want to understand the machinery, and headlines were never the point. Still, the drop into general availability feels abrupt. Years of work, and now suddenly it's everyone's problem, or opportunity.
Celebration meets immediate anxiety
The reaction was applause with a side of dread. One voice: "This is big… but I hope my security team doesn't see it yet." That's a warning disguised as humor, because once security teams catch on, backlogs grow and priorities shift. Another comment hinted at it: "Otherwise all existing work will stop until the 100 new tickets… get cleared."
There's a split second where innovation feels exciting, and then reality lands. Adoption is organizational as much as technical, and the organizational part is where things slow down.
The big idea: root without real power
Outside the Kubernetes deep end, the obvious question showed up quickly. One commenter asked it plainly: what is this for, and how does it improve security?
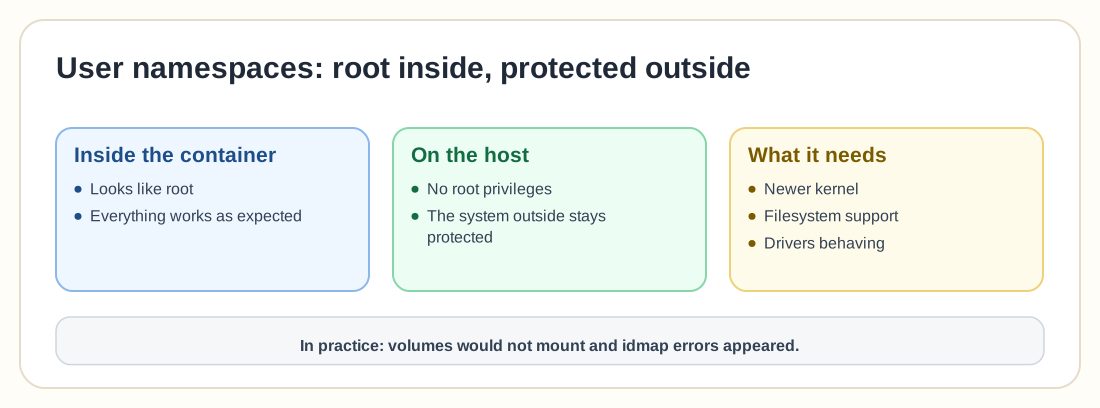
User namespaces let containers behave like they're running as root without holding root privileges on the host. It's a useful illusion, where everything inside works as expected and the system outside stays protected.
Some call it a huge win, "finally, real isolation without breaking workflows." Others push back: "It sounds great until it collides with everything else." A less vocal group is still trying to understand it.
Where theory collides with reality
The clean story cracks when people try it. One user enabled the feature and their volumes wouldn't mount at all, which is a hard stop. Another hit filesystem limitations, with errors tied to idmap support.
The feature depends on a stack of requirements: kernel versions, filesystem support, and drivers behaving correctly. The author says newer kernels should mostly work, but "should" is doing heavy lifting.
"It's new, rough edges are expected," runs the optimistic read. The cautious one: "If it breaks storage, it's not ready for production." A third camp waits for updates.
Builders vs. users: a familiar divide
There's a gap between the people who built this and the people who run it. The builder offers documentation, blog posts, and even talks explaining every layer, so it feels complete from that side.
Users live in messy environments, with different clusters, storage systems, and constraints. One comment captured that hesitation perfectly: they're "looking forward to trying it again" in a future version, not now. That comes from experience more than resistance, since most teams have been burned enough times to move carefully.
The shift no one can ignore
User namespaces are more than another feature toggle, because they change how people think about container security.
"This is what containers should have been from the start," says one take. "This will surface problems we've been ignoring," warns another. And some see both sides, recognizing that progress in systems like this always comes with a cost. Both camps are right: this makes systems safer, and it also breaks things, slows teams down, and forces hard decisions about priorities. Like most infrastructure changes, it doesn't ask for permission.